FOUND:Kroxigor 2.0 - SwampPuppy Edit
-
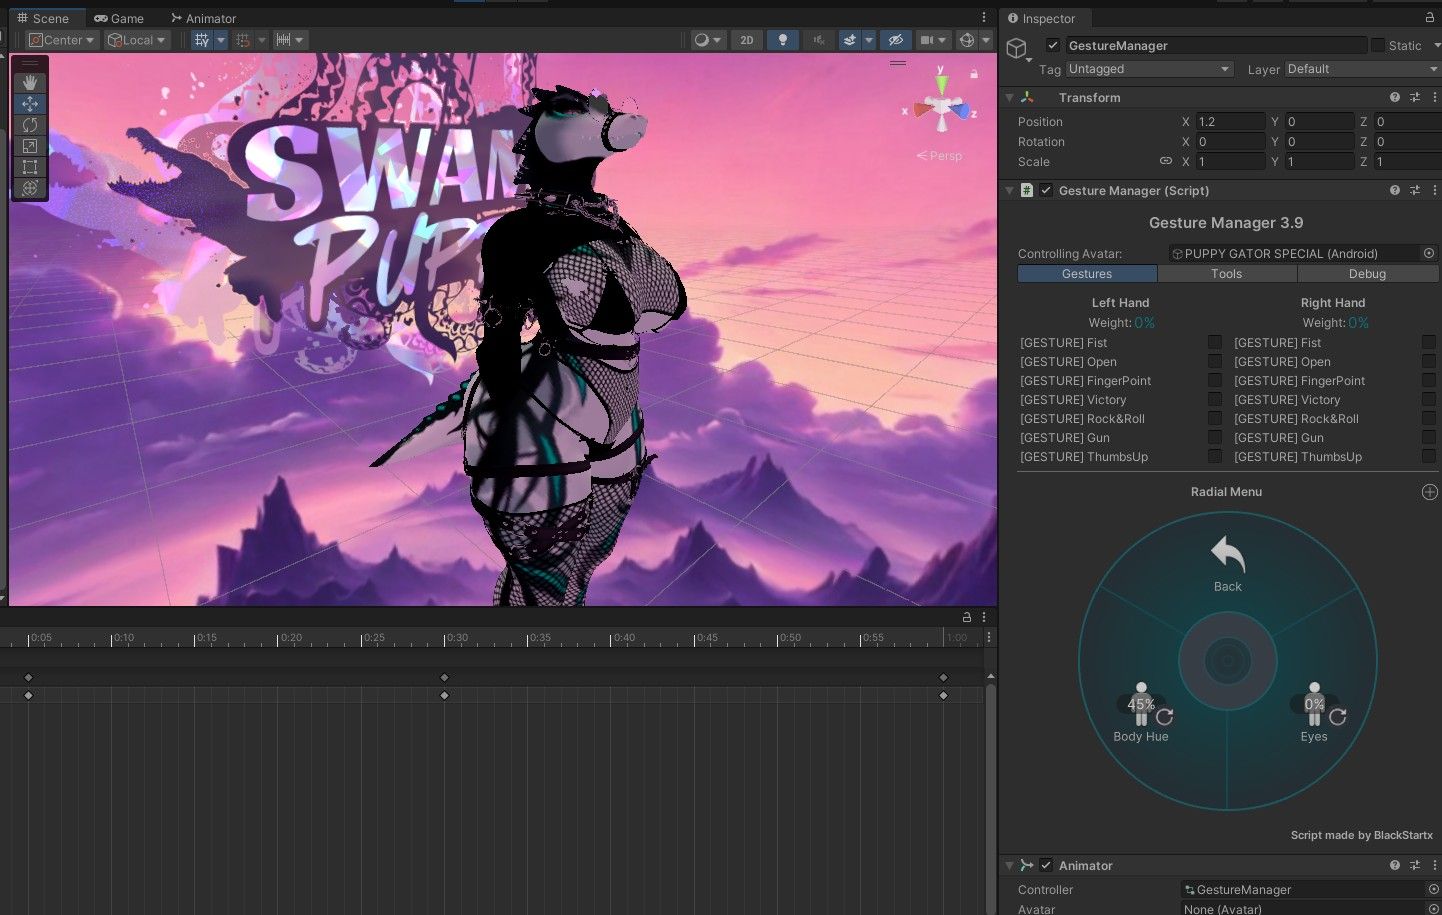
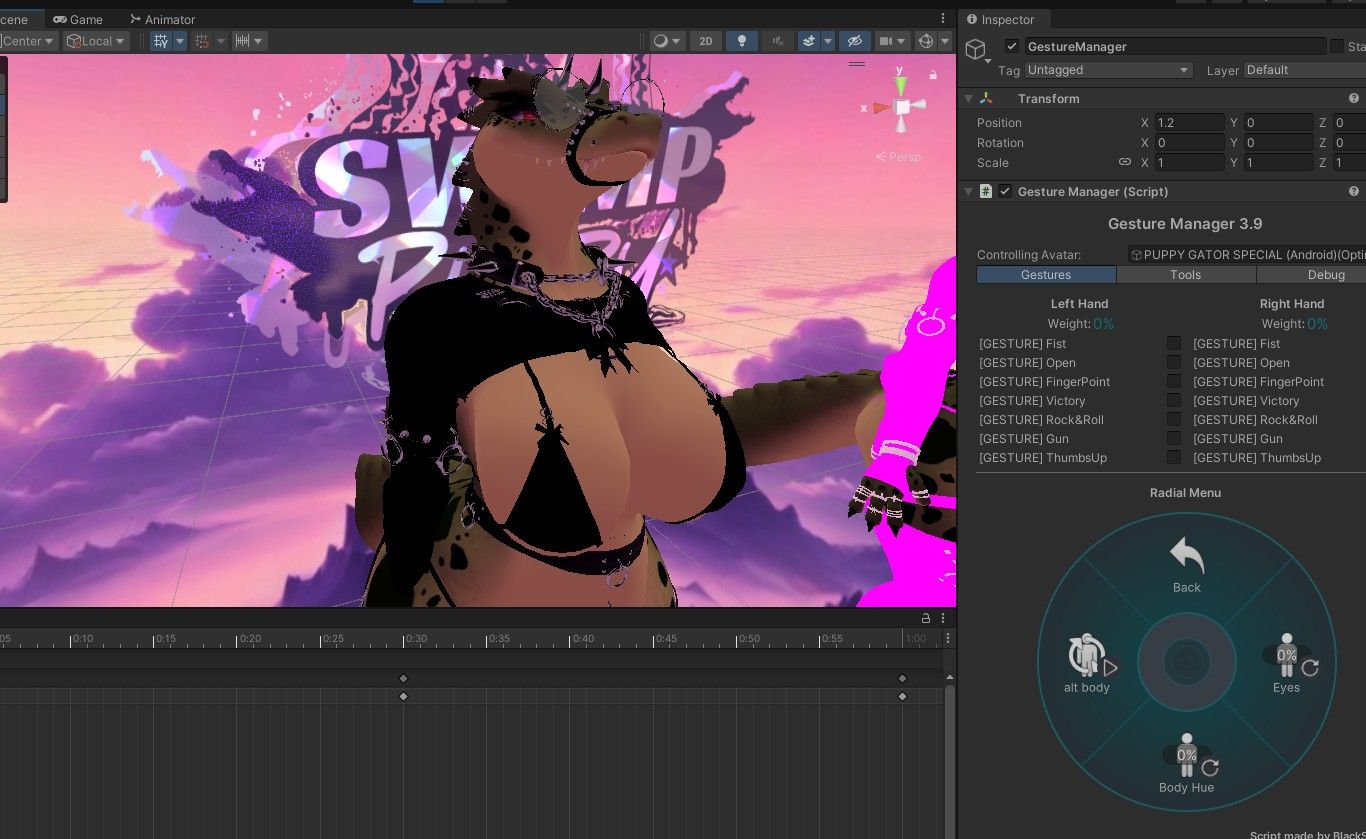
hueshift for quest -
alt body for quest on the same avi
-
!update!
im just starting over for a bit because1: i couldnt get some animations to work for me on quest
2: there was a lot of other stuff that i could add on the avatar like different jean colors and other things for the clothes
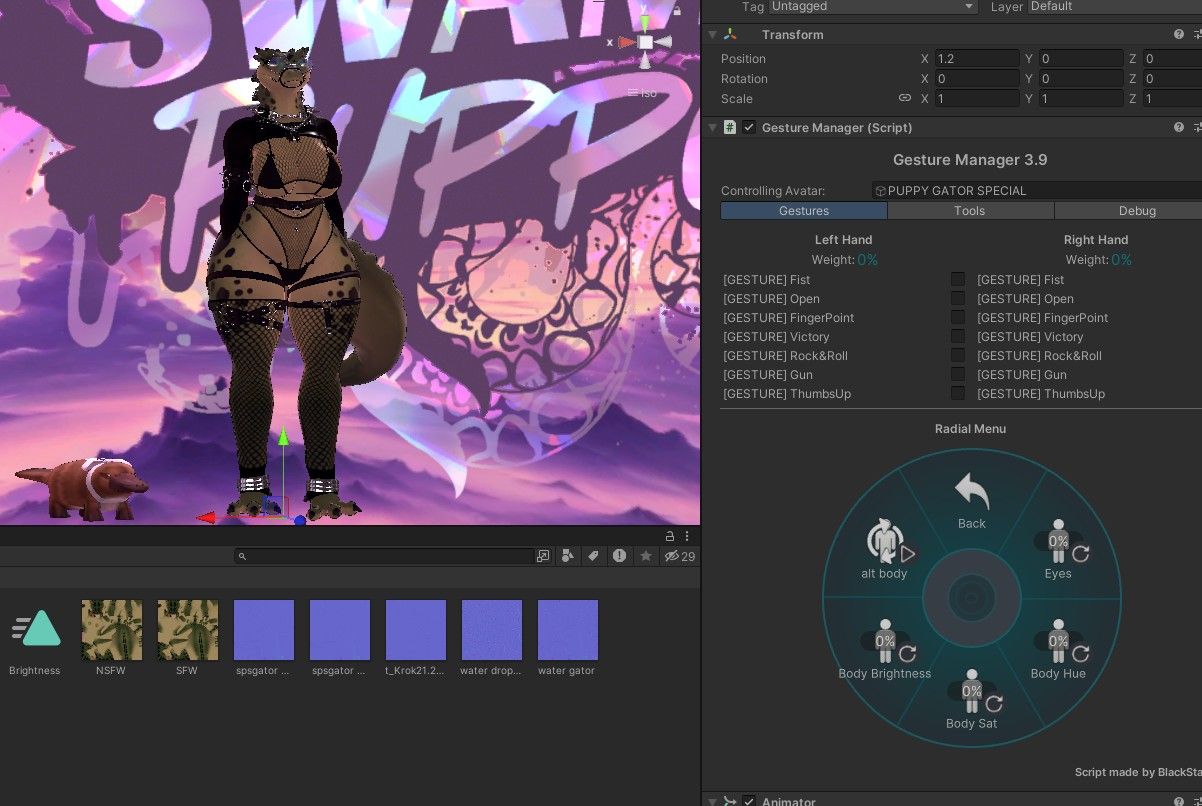
3: i can add more body stuff texture wise on the body so here is my progress atm since i started over
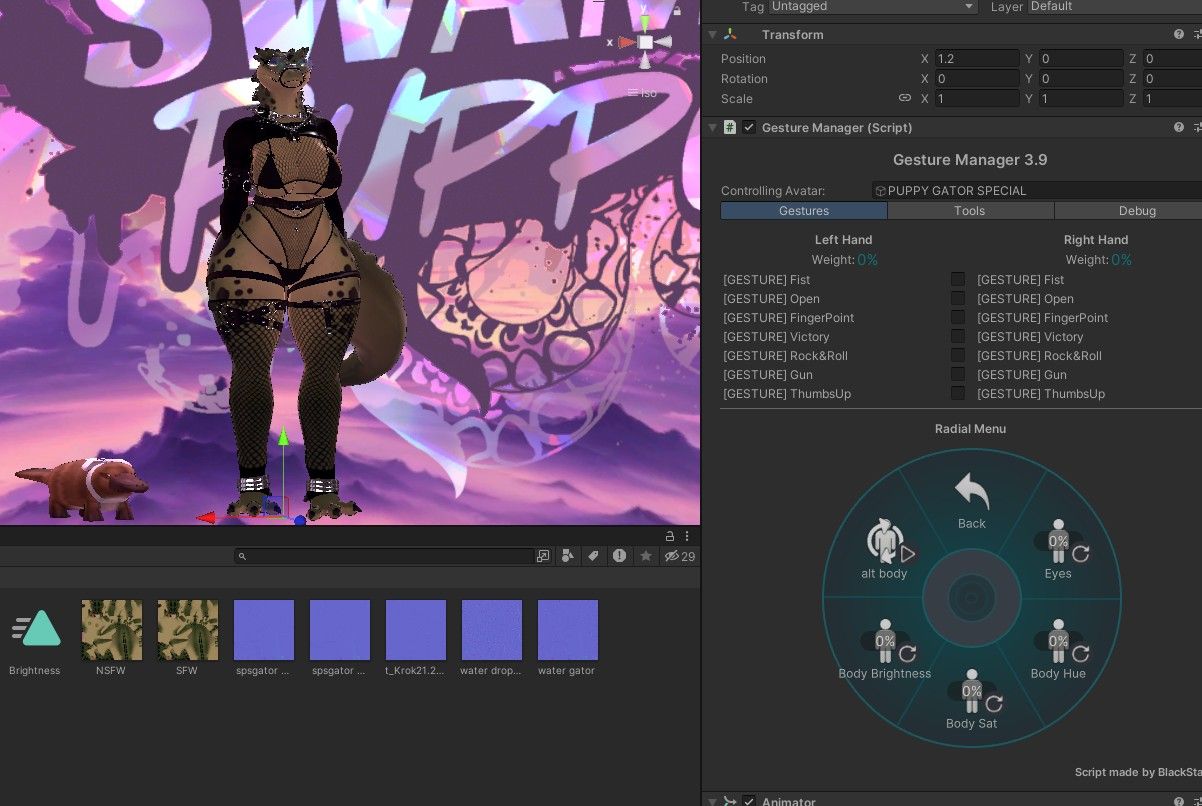
-
AND I DIDNT MEAN TO SEND A PHOTO TWICE
-
body hue is on the same slider for the main one
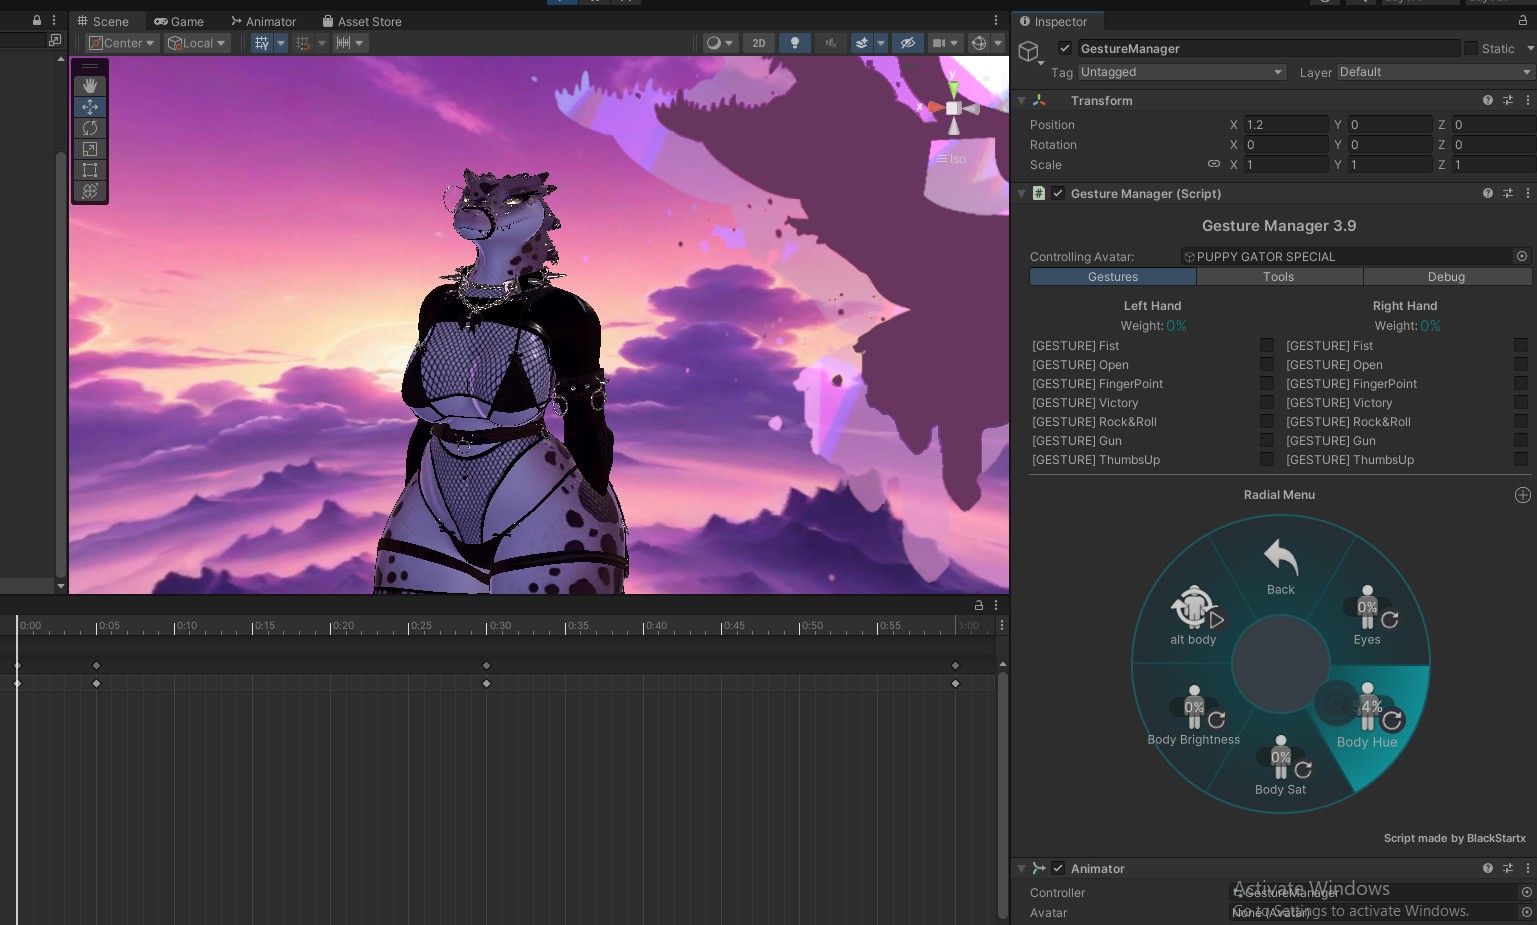
-
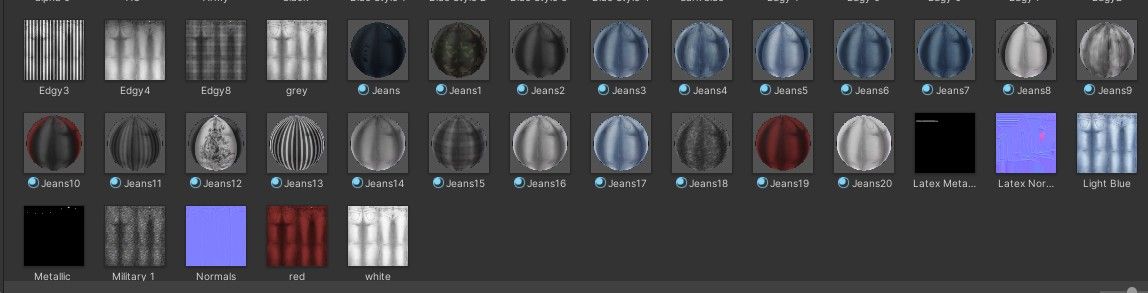 jeans material done now onto the animations
-
ALSO YOU MIGHT HAVE TO HAVE THE SWAMPPUPPY KROX IN YOUR PROJECT BEFORE IMPORTING THIS SINCE IT MIGHT RELOAD THE SCENE
-
first batch of the updated version, im making a quest version too
okay so this one didnt export the animations wait a sec
-
yes i am still doing the quest version btw because some of the animations are being weird
-
yes i am still doing the quest version btw because some of the animations are being weird
@masterofspace You got this! Thanks so much!
-
ive been putting files thru my scan tool for a while now and
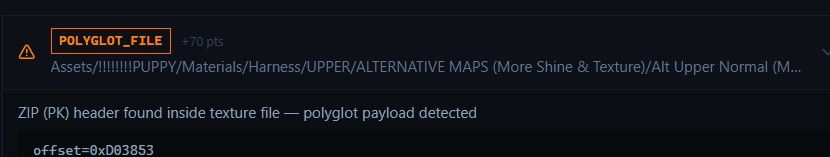 i have to genuinely ask why is there a polyglot payload attached to a single, random png texture in the files- does anyone know what it is before i even think about opening up the original edit in a project. the rest of the issues are simply alerts about unlit_wf info but this one has no actual info attached..
ETA: i scanned the one by @masterofspace to see if the polyglot thing was still in that one as well since they were working with the original and
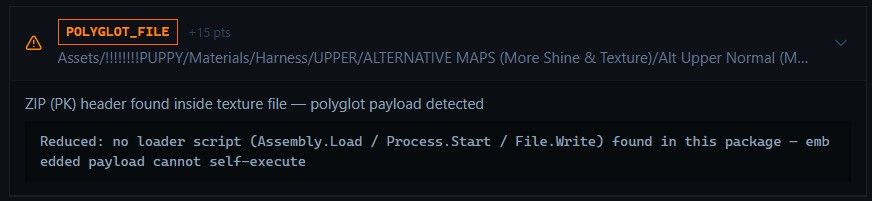
so what the hell is this supposed payload the original one has that masterofspace removed
Took one more look at the original
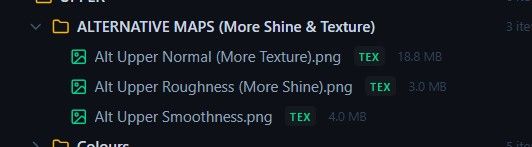 versus Space's
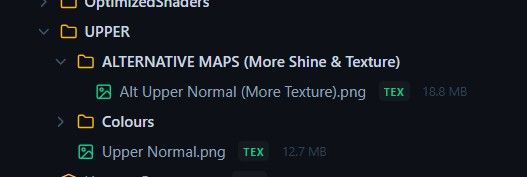 and space took out two of the textures
Is it the mapping information for the smoothness/roughness map that is a polyglot?
I am an avatar connoisseur, I love everything weird and strange, and world drops. Give me something to customize and my soul is yours!
Wishlist: https://drive.google.com/drive/folders/1GZ5wx6Bc2DAxX9vmd5TaVRZgFFnTnBEx?usp=sharing (UPDATED 3/18/2026)
If you know where to get any of them, @ me or send me a DM!
-
@claptasticfrag So, I've looked into the files and dissected its inner workings. It appears to be a false positive due to a funny lil math coincidence.
The .png appears to be compressed using zlib, to shrink its size. However, doing so generated a ton of random bytes, which out of chance generated a string that spells out something in the lines of "PK...." which is what being triggered as a zip. There's also a ton of other false positives.
It is highly unlikely for this file to contain any malicious payload. There is no central directory anywhere, CRC valid, no trailing garbage (no signs of tampering), consistent structure with images rather than something fishy.
If you recompress the .png it might not even be flagged again.
Obviously it is always natural and good to be wary of these kinds of things, which is why you should never blindly trust scripts.
Went a step further and did some deeper analysis, still no signs of a payload BUT it doesn't rule out a decoder-level exploit. But that would need to target a known vulnerability... -
ive been putting files thru my scan tool for a while now and
i have to genuinely ask why is there a polyglot payload attached to a single, random png texture in the files- does anyone know what it is before i even think about opening up the original edit in a project. the rest of the issues are simply alerts about unlit_wf info but this one has no actual info attached..ETA: i scanned the one by @masterofspace to see if the polyglot thing was still in that one as well since they were working with the original and
so what the hell is this supposed payload the original one has that masterofspace removed
Took one more look at the original
versus Space's and space took out two of the texturesIs it the mapping information for the smoothness/roughness map that is a polyglot?
@ClaptasticFrag so idk what a polygot is, but im guessing its a virus of some sorts.
-
@claptasticfrag So, I've looked into the files and dissected its inner workings. It appears to be a false positive due to a funny lil math coincidence.
The .png appears to be compressed using zlib, to shrink its size. However, doing so generated a ton of random bytes, which out of chance generated a string that spells out something in the lines of "PK...." which is what being triggered as a zip. There's also a ton of other false positives.
It is highly unlikely for this file to contain any malicious payload. There is no central directory anywhere, CRC valid, no trailing garbage (no signs of tampering), consistent structure with images rather than something fishy.
If you recompress the .png it might not even be flagged again.
Obviously it is always natural and good to be wary of these kinds of things, which is why you should never blindly trust scripts.
Went a step further and did some deeper analysis, still no signs of a payload BUT it doesn't rule out a decoder-level exploit. But that would need to target a known vulnerability...@Trident707 thank you for looking into it!! glad to know it's most likely just a bug in how some compressions work
-
DROPPING THE EXPANDED VERSION IN A FEW HOURS THO
-
@masterofspace ITS BEEN 5 HOURS I NEED IT
@meth-head
here, idk if this one can physically be quest. ive tried
-
@meth-head
here, idk if this one can physically be quest. ive tried
@masterofspace FFFFFFFFFFFFFFFFFUUUUUUUUUUUUUUCKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKKK ill try me best then





Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login