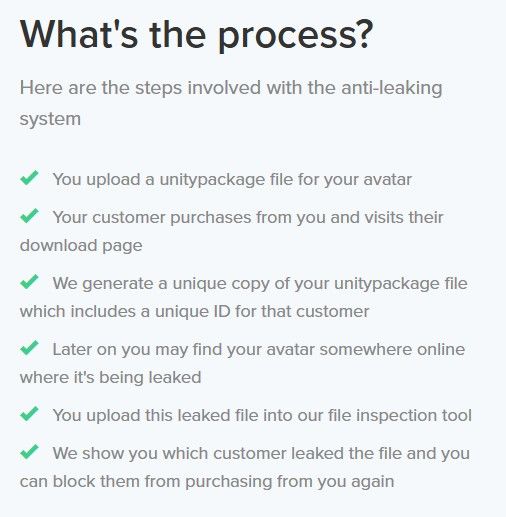
How does PayHip anti-leak feature work?
-
Bumping this because I am also curious
-
Probably because the files contain scripts inside. If it turns out that the files don't include a script, then they must contain some kind of metadata with the unique ID mentioned.
If anyone has a PayHip avatar file and would like to volunteer, please analyze the unitypackage with this tool and let us know the results in a reply.
-
Probably because the files contain scripts inside. If it turns out that the files don't include a script, then they must contain some kind of metadata with the unique ID mentioned.
If anyone has a PayHip avatar file and would like to volunteer, please analyze the unitypackage with this tool and let us know the results in a reply.
@anonberry Here are the results of some payhip / gumroad/jynxi avatars I have bought:
File:        \Downloads\yunos\Yuno_by_Mimiiu_V1.5 JANUARY 2026.unitypackage
SHA-256:     bc97aab039e5a329e5edb849fac41308f89f54521dc9f415c1d603b9e3002bdc
Size:        491.6 MB
Type:        UnityPackage
━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━

Assets: total=1873  | scripts=3  | dlls=0  | textures=445  | audio=6  | prefabs=17

FINDINGS (4 found)
────────────────────────────────────────────────────

[MEDIUM   +4] Meta file contains external object references (assets not included in package)
  File:      Assets/Yuno by Mimiiu/3.0/GogoLoco/Runtime/GoGo/GoModel/GoBadge/GoLogo.fbx
  ID:        META_EXTERNAL_REF

[MEDIUM   +4] Meta file contains external object references (assets not included in package)
  File:      Assets/Yuno by Mimiiu/3.0/GogoLoco/Runtime/GoGo/GoModel/GoBadge/GoLogo_Pin_FBX.fbx
  ID:        META_EXTERNAL_REF

[MEDIUM   +4] Meta file contains external object references (assets not included in package)
  File:      Assets/Yuno by Mimiiu/3.0/GogoLoco/Runtime/GoGo/GoModel/GoBone/GoFBX/GoBone_Coat.fbx
  ID:        META_EXTERNAL_REF

[MEDIUM   +4] Meta file contains external object references (assets not included in package)
  File:      Assets/Yuno by Mimiiu/3.0/GogoLoco/Runtime/GoGo/GoModel/GoBone/GoFBX/GoBone.fbx
  ID:        META_EXTERNAL_REF
────────────────────────────────────────────────────
Total score:   16
Risk level:    ■ CLEAN
Action:        AutoPublish
Duration:      2.63s
────────────────────────────────────────────────────

════════════════════════════════════════════════════
 VERDICT
════════════════════════════════════════════════════
 ✓  SAFE TO USE
    No significant security concerns were found.
    This package appears to be legitimate Unity content.
    You can install it normally.
File: \Downloads\Dahlia UPDATE2026.unitypackage SHA-256: bf134fbb3fd91d2baa598f080d1820520379c8e62e92f258bca5f56bcaddc5b6 Size: 488.7 MB Type: UnityPackage ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ Assets: total=1178 | scripts=0 | dlls=0 | textures=258 | audio=0 | prefabs=8 FINDINGS (3 found) ──────────────────────────────────────────────────── [MEDIUM +4] Meta file contains external object references (assets not included in package) File: Assets/GoGo/GoModel/GoBone/GoFBX/GoBone_Coat.fbx ID: META_EXTERNAL_REF [MEDIUM +4] Meta file contains external object references (assets not included in package) File: Assets/GoGo/GoModel/GoBadge/GoLogo.fbx ID: META_EXTERNAL_REF [MEDIUM +4] Meta file contains external object references (assets not included in package) File: Assets/GoGo/GoModel/GoBone/GoFBX/GoBone.fbx ID: META_EXTERNAL_REF ──────────────────────────────────────────────────── Total score: 12 Risk level: ■ CLEAN Action: AutoPublish Duration: 2.56s ──────────────────────────────────────────────────── ════════════════════════════════════════════════════ VERDICT ════════════════════════════════════════════════════ ✓ SAFE TO USE No significant security concerns were found. This package appears to be legitimate Unity content. You can install it normally.\Downloads\Eve By GeekieFox.unitypackage SHA-256: ce7ef4f766e40f7d3db7909b99b6c3d7afd9c66876d0b1761ca96c29c85e7589 Size: 1.3 GB Type: UnityPackage ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ Assets: total=1016 | scripts=0 | dlls=0 | textures=271 | audio=7 | prefabs=13 FINDINGS (3 found) ──────────────────────────────────────────────────── [MEDIUM +5] Prefab references an unusually large number of scripts File: Assets/AVI/Inner Works/Eve.prefab ID: PREFAB_MANY_SCRIPTS Context: count=167 [MEDIUM +5] Prefab references an unusually large number of scripts File: Assets/AVI/Inner Works/Eve FT.prefab ID: PREFAB_MANY_SCRIPTS Context: count=189 [MEDIUM +4] Meta file contains external object references (assets not included in package) File: Assets/AVI/Extras/_Flexuh Model 2024/Sex Toys/FBX/Flexuh_Dildo3.fbx ID: META_EXTERNAL_REF ──────────────────────────────────────────────────── Total score: 14 Risk level: ■ CLEAN Action: AutoPublish Duration: 6.79s ──────────────────────────────────────────────────── ════════════════════════════════════════════════════ VERDICT ════════════════════════════════════════════════════ ✓ SAFE TO USE No significant security concerns were found. This package appears to be legitimate Unity content. You can install it normally.\Downloads\Hi-Wire By GeekieFox.unitypackage SHA-256: d97cfceb12f1c34f3c73cfecee2f832c24a12d63e41d25e63a3d9945ba00f01d Size: 1.6 GB Type: UnityPackage ━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━ Assets: total=781 | scripts=0 | dlls=0 | textures=250 | audio=14 | prefabs=9 FINDINGS (3 found) ──────────────────────────────────────────────────── [HIGH +15] ZIP (PK) header found inside texture file — polyglot payload detected File: Assets/AVI/Mats/CLOTHES/Denim Jacket/CropDenim RIPPED 5_Base_color.png ID: POLYGLOT_FILE Context: Reduced: no loader script (Assembly.Load / Process.Start / File.Write) found in this package — embedded payload cannot self-execute [MEDIUM +5] Prefab references an unusually large number of scripts File: Assets/AVI/Inner Works/HI-Wire FT.prefab ID: PREFAB_MANY_SCRIPTS Context: count=155 [MEDIUM +5] Prefab references an unusually large number of scripts File: Assets/AVI/Inner Works/HI-Wire .prefab ID: PREFAB_MANY_SCRIPTS Context: count=155 ──────────────────────────────────────────────────── Total score: 25 Risk level: ■ CLEAN Action: AutoPublish Duration: 11.56s ──────────────────────────────────────────────────── ════════════════════════════════════════════════════ VERDICT ════════════════════════════════════════════════════ ✓ SAFE TO USE No significant security concerns were found. This package appears to be legitimate Unity content. You can install it normally.The first one of these claims to have payhip protection. Some others might, but none of them mention it. It appears the software has not detected anything. I investigated the first one. There are 3 scripts from gogoloco, and 1 script to load the scene ( I checked the load scene script, nothing there ).
I ran "strings" on the raw unitypackage file but I don't think I'll be able to find anything here, I have 0 clue how their backend scans these or how they encode anything.
Extracting the unitypackage does not reveal anything to me.
Same goes for another avatar "Nyxi by Cakeii"- that did not yield any results either.
It's also likely the identifier hash is baked into the file in some weird way, not just as a script.
-
Telling how your anti-leak system works isn't a good idea, is so easy to reverse engineer this, but very expensive to test it
@SummerTYT I agree. Would love to know if someone has access to this dashboard/utility from Payhip, just a simple test of comparing the cloned unitypackage + own unitypackage would reveal a good amount. Actually finding what they change would prolly be very hard without a lot of testing though.
-
@SummerTYT I agree. Would love to know if someone has access to this dashboard/utility from Payhip, just a simple test of comparing the cloned unitypackage + own unitypackage would reveal a good amount. Actually finding what they change would prolly be very hard without a lot of testing though.
@noemiwasse I was thinking in buying the same asset but with different accounts
-
bumping because I'm also curious
-
if you have no idea what the anti leak is there is a payhip video explaining what it does! it looks like it only shows who bought and shared the avatar. so anyone downloading will be okay (possibly? not too sure)
-
if you have no idea what the anti leak is there is a payhip video explaining what it does! it looks like it only shows who bought and shared the avatar. so anyone downloading will be okay (possibly? not too sure)
@ThatGirlNextDoor correct
-
From my own digging I have discovered that its a file structure renaming, when you go to donwload a .unitypackage from payhip, they clone it and rename the entire file structure to fileName(Number) and then sends that to you to download, that unique file data is then tied to your account somehow. Simply looking at 2 legit unity files of the same asset reveals this information.
Be sure to upvote if I was able to help out. Emojis don't help my rep. I am talking to you, the people who only react with emojis instead of actually upvoting if I was able to help.
-
From my own digging I have discovered that its a file structure renaming, when you go to donwload a .unitypackage from payhip, they clone it and rename the entire file structure to fileName(Number) and then sends that to you to download, that unique file data is then tied to your account somehow. Simply looking at 2 legit unity files of the same asset reveals this information.
I am still digging more into this, and right now I am waiting to get approved for payhips anti leak system, if I can get access to that then I can run my own tests with my own uploaded assets to figure out ways to bypass this, right now I have a few ideas of ways around it but no real method to test it without risk ATM.
Be sure to upvote if I was able to help out. Emojis don't help my rep. I am talking to you, the people who only react with emojis instead of actually upvoting if I was able to help.
-
I am still digging more into this, and right now I am waiting to get approved for payhips anti leak system, if I can get access to that then I can run my own tests with my own uploaded assets to figure out ways to bypass this, right now I have a few ideas of ways around it but no real method to test it without risk ATM.
@Shadowkurou @summertyt
-
I am still digging more into this, and right now I am waiting to get approved for payhips anti leak system, if I can get access to that then I can run my own tests with my own uploaded assets to figure out ways to bypass this, right now I have a few ideas of ways around it but no real method to test it without risk ATM.
@Shadowkurou I can help you with that, we can use my scanner to check differences between those unitypackages
-
@Shadowkurou I can help you with that, we can use my scanner to check differences between those unitypackages
@SummerTYT I used winmerge to compare the files directly between 2 legit copys of the .unitypackage the difference was the naming, I also checked the .asset files for differences and those are identical, nothing of the physical assets were changed, the only difference I was able to directly find was every single asset in the package had an added number to it. If I can manage to get access to the anti-leak feature on payhip then thats how I plan on testing things to see if my method actually works. If my method does work then I will share it here, or if someone already has access to that system and is willing to help out.
-
Eight months, three bumps, and the rest of the kit is strings and WinMerge. So here's what you're actually up against, free, on the house.
Note that these aren't necessarily done by Payhip, but i figure you guys have a ChatGPT subscription and can verify these methods actually exist:
- Payloads spread across hundreds of assets with error correction. Scrub half and the watermark still rebuilds itself.
- Frequency-domain marks in textures that ride straight through resize and recompress, so the re-export plan does nothing.
- Sub-visual float dithering on mesh vertices. Survives reimport into Unity or Blender, invisible to your eyes and to your diff tool.
- Zero-width and homoglyph payloads in text and shaders that no editor you own will even render.
- Blind extraction. No clean copy needed for comparison. They read the ID straight out of yours.
And then there's the scanner, which is the funniest thing in this whole thread.
 It's hard to believe that the same someone who put together that malware scanner is now pointing HIS OWN TOOL at finding fingerprints. Like, I hardly believe you're the actual author. It's either that, or you racked up some hefty Gemini bills (yeah, I saw your proud GitHub Gemini AI Camo).
What it does:
- Draws hand-rolled ASCII boxes and sums a pile of "points" into a five-rung ladder: CLEAN, LIKELY SAFE, REVIEW RECOMMENDED, NOT RECOMMENDED, DO NOT INSTALL.
- For anything that lands on CLEAN, prints "✓ SAFE TO USE" and "You can install it normally." Its machine-readable verdict for CLEAN is, no joke, the literal string "AutoPublish."
- Has no file-size logic anywhere in the scoring. A 491MB avatar gets its size printed in the header and then completely ignored, so a clean-looking 491MB package sails straight to "You can install it normally."
- Flags ordinary external object references (the externalObjects entry in a .meta, exactly what GogoLoco leans on) as MEDIUM, worth a whole 4 points.
What it actually hunts for is Process.Start, Assembly.Load(bytes), [DllImport], PE section entropy, and MZ/PK headers stuffed inside textures: textbook antivirus signature matching.
Which is exactly what makes his own offer, from up the thread, so funny:
@SummerTYT said:
@Shadowkurou I can help you with that, we can use my scanner to check differences between those unitypackagesWhat it has zero lines of code for: any watermark, any fingerprint, any LSB or DCT or frequency-domain read, any mesh-vertex inspection, any per-asset GUID consistency check, any diff between two copies.
And here's the part I'll be fair about, because it makes the rest worse, not better. The scanner itself does what it advertises: it's competent malware static analysis.
That's not a "learn to program" problem, it's a lane problem. Being good at "will this run code on my machine" buys you nothing on "is this file fingerprinted." Antivirus and forensic watermarking barely share a vocabulary: one hunts executable behavior, the other hunts a statistical signal spread across the asset data. You built a strong tool for the wrong question and walked it into a room where only the other question matters.
And linking your GitHub isn't the flex you think it is. A malware scanner is a well-paved road any AI model has seen ten thousand times and will hand you on request. Forensic watermarking is the opposite, adversarial and niche, built on coding theory that doesn't fall out of autocomplete. The part that was easy to generate is the part that was never going to matter here.
And you walked into this after warning everyone else off it.
@SummerTYT said:
Telling how your anti-leak system works isn't a good idea, is so easy to reverse engineer this, but very expensive to test itLaughing emoji and all. And "easy to reverse engineer" is the confession folded into the boast, because both horns gut you. If Gemini wrote that scanner, you don't have the RE chops you're claiming. And if you hand-built it, you of all people know it just reads metadata and greps for base64 blobs, and you held that up to crack a fingerprint. You literally brought a crowbar to a bank vault. It reads as someone who's never written a line of code his agent didn't write for him.
@SummerTYT said:
I was thinking in buying the same asset but with different accountsPair that statement with the scanner-diff offer up the thread (#14) and you've reinvented the collusion attack, the oldest move in the watermarking literature, and the exact one any serious fingerprinting scheme is built from the ground up to survive (go read about Tardos codes). Back in #4 you called it "expensive to test." Here in #7 you volunteer to go pay exactly that, the stack of duplicate purchases, to run the one method competent marking is specifically designed to outlast.
And the offer is hollow on the tool's own terms: a comparison tool with no diff mode, aimed at an attack you already called too expensive to win, against a mark it has no code to even see. The "AutoPublish" verdict is the bow on top: a label that literally says ship it, on the one axis it's structurally blind to, the exact axis that identifies you.
@Shadowkurou said:
I used winmerge to compare the files directly between 2 legit copys of the .unitypackage the difference was the naming, I also checked the .asset files for differences and those are identical, nothing of the physical assets were changed, the only difference I was able to directly find was every single asset in the package had an added number to it. If I can manage to get access to the anti-leak feature on payhip then thats how I plan on testing things to see if my method actually works. If my method does work then I will share it here, or if someone already has access to that system and is willing to help out.@Shadowkurou you diffed two copies, saw that every asset got a number bolted onto it, decided the assets themselves were "identical," and now you're sitting in a queue for Payhip to approve you so you can test a method against a watermark you haven't even located. The renaming is the part they let you find. It's bait. The watermark is sitting in the files you just pronounced identical. That's literally what any competent watermarking does, it doesn't show on a vibe-coded tool or most tools on the market. It requires hands-on work with forensic tools or access to the source-code of the anti-leak to see what it does.
One last thing. That anti-leak access you're queued up for is not something to look forward to. It's gated behind an actual sales record and standing as a legitimate seller, specifically so it stays out of the hands of people exactly like you. And even if you had access, all it gets you is an oracle, not an answer. Upload your own protected asset, mutate a copy, resubmit, watch whether it still fingerprints you, repeat until it stops triggering. In practice you'd be running it through a submit-a-leak-get-a-name workflow that was never built to be queried like that, slow and logged, spending a seller account tied to your real sales record on every single probe. You're not going to oracle your way through a watermark with the same toolkit that couldn't even find it. And even if you did manage to do that, they most likely have systems in place to flag that exact behavior.
Sit with what you did here: you went onto a leak forum and publicly announced you want into their anti-piracy system so you can break it. They have eyes, you know. You might not have the same username or any ties between this ripper account and your Payhip, but you weren't that difficult to find bro.
-
Eight months, three bumps, and the rest of the kit is strings and WinMerge. So here's what you're actually up against, free, on the house.
Note that these aren't necessarily done by Payhip, but i figure you guys have a ChatGPT subscription and can verify these methods actually exist:
- Payloads spread across hundreds of assets with error correction. Scrub half and the watermark still rebuilds itself.
- Frequency-domain marks in textures that ride straight through resize and recompress, so the re-export plan does nothing.
- Sub-visual float dithering on mesh vertices. Survives reimport into Unity or Blender, invisible to your eyes and to your diff tool.
- Zero-width and homoglyph payloads in text and shaders that no editor you own will even render.
- Blind extraction. No clean copy needed for comparison. They read the ID straight out of yours.
And then there's the scanner, which is the funniest thing in this whole thread.
It's hard to believe that the same someone who put together that malware scanner is now pointing HIS OWN TOOL at finding fingerprints. Like, I hardly believe you're the actual author. It's either that, or you racked up some hefty Gemini bills (yeah, I saw your proud GitHub Gemini AI Camo).What it does:
- Draws hand-rolled ASCII boxes and sums a pile of "points" into a five-rung ladder: CLEAN, LIKELY SAFE, REVIEW RECOMMENDED, NOT RECOMMENDED, DO NOT INSTALL.
- For anything that lands on CLEAN, prints "✓ SAFE TO USE" and "You can install it normally." Its machine-readable verdict for CLEAN is, no joke, the literal string "AutoPublish."
- Has no file-size logic anywhere in the scoring. A 491MB avatar gets its size printed in the header and then completely ignored, so a clean-looking 491MB package sails straight to "You can install it normally."
- Flags ordinary external object references (the externalObjects entry in a .meta, exactly what GogoLoco leans on) as MEDIUM, worth a whole 4 points.
What it actually hunts for is Process.Start, Assembly.Load(bytes), [DllImport], PE section entropy, and MZ/PK headers stuffed inside textures: textbook antivirus signature matching.
Which is exactly what makes his own offer, from up the thread, so funny:
@SummerTYT said:
@Shadowkurou I can help you with that, we can use my scanner to check differences between those unitypackagesWhat it has zero lines of code for: any watermark, any fingerprint, any LSB or DCT or frequency-domain read, any mesh-vertex inspection, any per-asset GUID consistency check, any diff between two copies.
And here's the part I'll be fair about, because it makes the rest worse, not better. The scanner itself does what it advertises: it's competent malware static analysis.
That's not a "learn to program" problem, it's a lane problem. Being good at "will this run code on my machine" buys you nothing on "is this file fingerprinted." Antivirus and forensic watermarking barely share a vocabulary: one hunts executable behavior, the other hunts a statistical signal spread across the asset data. You built a strong tool for the wrong question and walked it into a room where only the other question matters.
And linking your GitHub isn't the flex you think it is. A malware scanner is a well-paved road any AI model has seen ten thousand times and will hand you on request. Forensic watermarking is the opposite, adversarial and niche, built on coding theory that doesn't fall out of autocomplete. The part that was easy to generate is the part that was never going to matter here.
And you walked into this after warning everyone else off it.
@SummerTYT said:
Telling how your anti-leak system works isn't a good idea, is so easy to reverse engineer this, but very expensive to test itLaughing emoji and all. And "easy to reverse engineer" is the confession folded into the boast, because both horns gut you. If Gemini wrote that scanner, you don't have the RE chops you're claiming. And if you hand-built it, you of all people know it just reads metadata and greps for base64 blobs, and you held that up to crack a fingerprint. You literally brought a crowbar to a bank vault. It reads as someone who's never written a line of code his agent didn't write for him.
@SummerTYT said:
I was thinking in buying the same asset but with different accountsPair that statement with the scanner-diff offer up the thread (#14) and you've reinvented the collusion attack, the oldest move in the watermarking literature, and the exact one any serious fingerprinting scheme is built from the ground up to survive (go read about Tardos codes). Back in #4 you called it "expensive to test." Here in #7 you volunteer to go pay exactly that, the stack of duplicate purchases, to run the one method competent marking is specifically designed to outlast.
And the offer is hollow on the tool's own terms: a comparison tool with no diff mode, aimed at an attack you already called too expensive to win, against a mark it has no code to even see. The "AutoPublish" verdict is the bow on top: a label that literally says ship it, on the one axis it's structurally blind to, the exact axis that identifies you.
@Shadowkurou said:
I used winmerge to compare the files directly between 2 legit copys of the .unitypackage the difference was the naming, I also checked the .asset files for differences and those are identical, nothing of the physical assets were changed, the only difference I was able to directly find was every single asset in the package had an added number to it. If I can manage to get access to the anti-leak feature on payhip then thats how I plan on testing things to see if my method actually works. If my method does work then I will share it here, or if someone already has access to that system and is willing to help out.@Shadowkurou you diffed two copies, saw that every asset got a number bolted onto it, decided the assets themselves were "identical," and now you're sitting in a queue for Payhip to approve you so you can test a method against a watermark you haven't even located. The renaming is the part they let you find. It's bait. The watermark is sitting in the files you just pronounced identical. That's literally what any competent watermarking does, it doesn't show on a vibe-coded tool or most tools on the market. It requires hands-on work with forensic tools or access to the source-code of the anti-leak to see what it does.
One last thing. That anti-leak access you're queued up for is not something to look forward to. It's gated behind an actual sales record and standing as a legitimate seller, specifically so it stays out of the hands of people exactly like you. And even if you had access, all it gets you is an oracle, not an answer. Upload your own protected asset, mutate a copy, resubmit, watch whether it still fingerprints you, repeat until it stops triggering. In practice you'd be running it through a submit-a-leak-get-a-name workflow that was never built to be queried like that, slow and logged, spending a seller account tied to your real sales record on every single probe. You're not going to oracle your way through a watermark with the same toolkit that couldn't even find it. And even if you did manage to do that, they most likely have systems in place to flag that exact behavior.
Sit with what you did here: you went onto a leak forum and publicly announced you want into their anti-piracy system so you can break it. They have eyes, you know. You might not have the same username or any ties between this ripper account and your Payhip, but you weren't that difficult to find bro.
@Helgelending I admit I was very arrogant in my reply, making assumptions, being sure about something whose complexity I hadn’t even imagined. It’s good to get a reality check from a well-informed person (or from a student/researcher/someone who works in the field in question if that’s your case).
I just want to tell you that @summertyt isn’t the person you think he is. I believe that we were arrogant in our statements, full of certainty and deep ignorance, but I also believe that doesn't mean he is a selfish person at heart.
It’s true that AI was used to assist in the development of his tool (and you may indeed have issues with that), but he didn’t create it to boost his own ego, he created it because he wants to help people. The same goes for his other works, because work isn’t just about technical quality, it’s about expression and intentions, too.
The words you used to talk about his works weren't meant as criticism; they were meant to invalidate what he takes pride in. On that point, I disagree with you. But still, I thank you for the reality check you gave me tonight.
-
@noemiwasse @shadowkurou Let's just give up on this, it doesn't make sense. Not only do we lack the knowledge and ability to break the system, but even if we did, it would be like fighting a hydra. This is unreal.
-
@Shadowkurou I can help you with that, we can use my scanner to check differences between those unitypackages
@SummerTYT If you can send those files to me as well, I'd appreciate it. I can try and see what I can find.
-
Eight months, three bumps, and the rest of the kit is strings and WinMerge. So here's what you're actually up against, free, on the house.
Note that these aren't necessarily done by Payhip, but i figure you guys have a ChatGPT subscription and can verify these methods actually exist:
- Payloads spread across hundreds of assets with error correction. Scrub half and the watermark still rebuilds itself.
- Frequency-domain marks in textures that ride straight through resize and recompress, so the re-export plan does nothing.
- Sub-visual float dithering on mesh vertices. Survives reimport into Unity or Blender, invisible to your eyes and to your diff tool.
- Zero-width and homoglyph payloads in text and shaders that no editor you own will even render.
- Blind extraction. No clean copy needed for comparison. They read the ID straight out of yours.
And then there's the scanner, which is the funniest thing in this whole thread.
It's hard to believe that the same someone who put together that malware scanner is now pointing HIS OWN TOOL at finding fingerprints. Like, I hardly believe you're the actual author. It's either that, or you racked up some hefty Gemini bills (yeah, I saw your proud GitHub Gemini AI Camo).What it does:
- Draws hand-rolled ASCII boxes and sums a pile of "points" into a five-rung ladder: CLEAN, LIKELY SAFE, REVIEW RECOMMENDED, NOT RECOMMENDED, DO NOT INSTALL.
- For anything that lands on CLEAN, prints "✓ SAFE TO USE" and "You can install it normally." Its machine-readable verdict for CLEAN is, no joke, the literal string "AutoPublish."
- Has no file-size logic anywhere in the scoring. A 491MB avatar gets its size printed in the header and then completely ignored, so a clean-looking 491MB package sails straight to "You can install it normally."
- Flags ordinary external object references (the externalObjects entry in a .meta, exactly what GogoLoco leans on) as MEDIUM, worth a whole 4 points.
What it actually hunts for is Process.Start, Assembly.Load(bytes), [DllImport], PE section entropy, and MZ/PK headers stuffed inside textures: textbook antivirus signature matching.
Which is exactly what makes his own offer, from up the thread, so funny:
@SummerTYT said:
@Shadowkurou I can help you with that, we can use my scanner to check differences between those unitypackagesWhat it has zero lines of code for: any watermark, any fingerprint, any LSB or DCT or frequency-domain read, any mesh-vertex inspection, any per-asset GUID consistency check, any diff between two copies.
And here's the part I'll be fair about, because it makes the rest worse, not better. The scanner itself does what it advertises: it's competent malware static analysis.
That's not a "learn to program" problem, it's a lane problem. Being good at "will this run code on my machine" buys you nothing on "is this file fingerprinted." Antivirus and forensic watermarking barely share a vocabulary: one hunts executable behavior, the other hunts a statistical signal spread across the asset data. You built a strong tool for the wrong question and walked it into a room where only the other question matters.
And linking your GitHub isn't the flex you think it is. A malware scanner is a well-paved road any AI model has seen ten thousand times and will hand you on request. Forensic watermarking is the opposite, adversarial and niche, built on coding theory that doesn't fall out of autocomplete. The part that was easy to generate is the part that was never going to matter here.
And you walked into this after warning everyone else off it.
@SummerTYT said:
Telling how your anti-leak system works isn't a good idea, is so easy to reverse engineer this, but very expensive to test itLaughing emoji and all. And "easy to reverse engineer" is the confession folded into the boast, because both horns gut you. If Gemini wrote that scanner, you don't have the RE chops you're claiming. And if you hand-built it, you of all people know it just reads metadata and greps for base64 blobs, and you held that up to crack a fingerprint. You literally brought a crowbar to a bank vault. It reads as someone who's never written a line of code his agent didn't write for him.
@SummerTYT said:
I was thinking in buying the same asset but with different accountsPair that statement with the scanner-diff offer up the thread (#14) and you've reinvented the collusion attack, the oldest move in the watermarking literature, and the exact one any serious fingerprinting scheme is built from the ground up to survive (go read about Tardos codes). Back in #4 you called it "expensive to test." Here in #7 you volunteer to go pay exactly that, the stack of duplicate purchases, to run the one method competent marking is specifically designed to outlast.
And the offer is hollow on the tool's own terms: a comparison tool with no diff mode, aimed at an attack you already called too expensive to win, against a mark it has no code to even see. The "AutoPublish" verdict is the bow on top: a label that literally says ship it, on the one axis it's structurally blind to, the exact axis that identifies you.
@Shadowkurou said:
I used winmerge to compare the files directly between 2 legit copys of the .unitypackage the difference was the naming, I also checked the .asset files for differences and those are identical, nothing of the physical assets were changed, the only difference I was able to directly find was every single asset in the package had an added number to it. If I can manage to get access to the anti-leak feature on payhip then thats how I plan on testing things to see if my method actually works. If my method does work then I will share it here, or if someone already has access to that system and is willing to help out.@Shadowkurou you diffed two copies, saw that every asset got a number bolted onto it, decided the assets themselves were "identical," and now you're sitting in a queue for Payhip to approve you so you can test a method against a watermark you haven't even located. The renaming is the part they let you find. It's bait. The watermark is sitting in the files you just pronounced identical. That's literally what any competent watermarking does, it doesn't show on a vibe-coded tool or most tools on the market. It requires hands-on work with forensic tools or access to the source-code of the anti-leak to see what it does.
One last thing. That anti-leak access you're queued up for is not something to look forward to. It's gated behind an actual sales record and standing as a legitimate seller, specifically so it stays out of the hands of people exactly like you. And even if you had access, all it gets you is an oracle, not an answer. Upload your own protected asset, mutate a copy, resubmit, watch whether it still fingerprints you, repeat until it stops triggering. In practice you'd be running it through a submit-a-leak-get-a-name workflow that was never built to be queried like that, slow and logged, spending a seller account tied to your real sales record on every single probe. You're not going to oracle your way through a watermark with the same toolkit that couldn't even find it. And even if you did manage to do that, they most likely have systems in place to flag that exact behavior.
Sit with what you did here: you went onto a leak forum and publicly announced you want into their anti-piracy system so you can break it. They have eyes, you know. You might not have the same username or any ties between this ripper account and your Payhip, but you weren't that difficult to find bro.
@Helgelending Excuse me but is this an AI-generated "roast"? The base goal here is to find what changes when you upload it via payhip. It's nothing crazy and I don't know why you're flaming the malware checker. The malware checker has no place here at all, this is a completely different topic. I used that just in-case it did find something of interest but the code was never meant for it.
-
@noemiwasse @shadowkurou Let's just give up on this, it doesn't make sense. Not only do we lack the knowledge and ability to break the system, but even if we did, it would be like fighting a hydra. This is unreal.
@anonberry I don't plan on giving up, just because one person thinks they know shit/ claims to know shit and only talks down on everyone does not mean I am going to give up. Iv made it through life through trial and error, if one thing does not work then I get back to it and try again till I see results.
@helgelending Bro I have no idea what crawled up your ass, but sitting here trying to shit on everyone is not the way, instead try to help and contribute.
Be sure to upvote if I was able to help out. Emojis don't help my rep. I am talking to you, the people who only react with emojis instead of actually upvoting if I was able to help.



Hello! It looks like you're interested in this conversation, but you don't have an account yet.
Getting fed up of having to scroll through the same posts each visit? When you register for an account, you'll always come back to exactly where you were before, and choose to be notified of new replies (either via email, or push notification). You'll also be able to save bookmarks and upvote posts to show your appreciation to other community members.
With your input, this post could be even better 💗
Register Login